The Invisible Chain: How Proprietary CDN Dependencies Are Holding Your Business Continuity Hostage
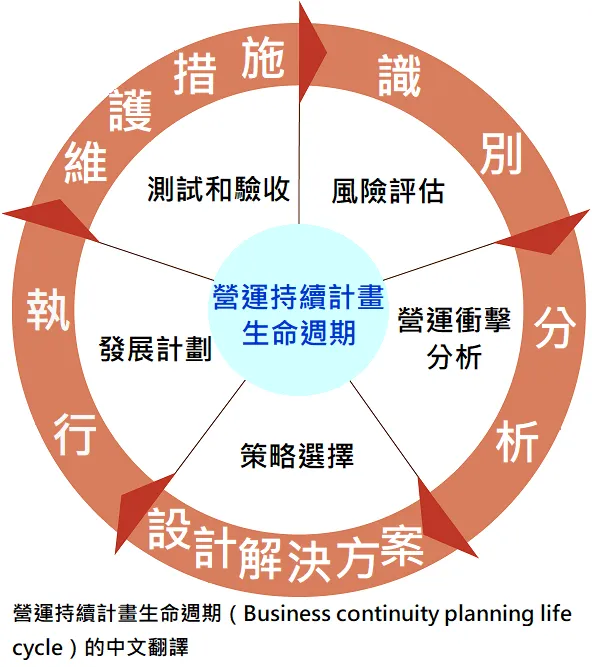
Photo: Z7504, CC BY-SA 4.0, via Wikimedia Commons
Every enterprise business continuity plan contains a section on vendor redundancy. It describes, usually in reassuring detail, how the organization maintains relationships with multiple CDN providers, how traffic can be rerouted within minutes of a primary provider failure, and how no single vendor relationship represents a single point of failure.
Most of those plans are fiction.
Not intentionally so. The engineers who wrote them believed what they were documenting. The problem is that CDN vendor lock-in has become sophisticated enough to be nearly invisible during normal operations — and catastrophically apparent only when a disaster forces an organization to actually execute the failover it thought it had prepared for.
The Lock-In That Hides in Plain Sight
Conventional discussions of vendor lock-in focus on contract terms: early termination fees, minimum volume commitments, notice periods measured in quarters rather than weeks. These are real constraints, but they are also the ones that procurement and legal teams are trained to scrutinize. The more dangerous dependencies live elsewhere.
Proprietary CDN implementations embed lock-in at the technical layer in ways that accumulate gradually and are rarely audited until a crisis forces the question. Configuration schemas that use vendor-specific syntax cannot be ported to a competing platform without complete reconstruction. Custom routing rules written against a proprietary API become inoperable the moment that API is unavailable. SSL certificate management workflows integrated with a single provider's tooling create operational gaps the moment that provider is unreachable.
Each of these dependencies, taken individually, appears manageable. Collectively, they form a chain that binds an enterprise to a single vendor far more effectively than any contract clause.
The Multi-Vendor Illusion
Many US enterprises believe they have addressed lock-in risk by maintaining accounts with two or more CDN providers. On paper, this constitutes redundancy. In practice, it frequently constitutes the appearance of redundancy without the substance.
The test is not whether a second vendor account exists. The test is whether a complete failover — one that preserves performance characteristics, routing logic, security configurations, and cache behavior — can be executed under realistic disaster conditions, at the speed that a genuine outage demands.
Organizations that have conducted honest tabletop exercises of this scenario frequently discover that their secondary CDN relationship is configured for a fraction of their actual traffic load, that their DNS failover logic has not been tested against real propagation delays, and that their operational runbooks reference tooling and processes that are specific to their primary vendor's environment. The second vendor account is real. The failover capability is not.
What Contracts Do Not Tell You
CDN contracts deserve scrutiny beyond their financial terms, but most enterprise procurement processes do not extend the analysis far enough. The questions that matter most are not about price or service level agreements — they are about data portability, configuration exportability, and API standardization.
Does the contract provide access to log data in a format that is portable to a competing analytics platform? Are configuration exports available in an open schema, or only in a proprietary format that requires vendor tooling to interpret? If the relationship terminates — voluntarily or otherwise — what is the operational timeline for reconstructing equivalent configurations in a new environment?
These questions are rarely asked during vendor selection. They become urgently relevant when a contract dispute, a vendor acquisition, or a major service failure forces an organization to answer them under pressure.
When Market Conditions Shift the Calculus
Business continuity planning typically focuses on infrastructure failures — outages, cyberattacks, natural disasters. But vendor lock-in creates a parallel category of risk that is easy to overlook: the risk that market conditions change in ways that make your current vendor relationship untenable, and that your technical dependencies prevent you from responding.
CDN pricing structures are not static. A vendor that offers competitive rates at current traffic volumes may become significantly more expensive as traffic grows, particularly if contract terms include tiered pricing that was not fully modeled at signing. Organizations that have embedded deep technical dependencies during a period of favorable pricing find that those dependencies constrain their negotiating leverage precisely when they need it most.
Similarly, CDN vendors are acquired, merged, and occasionally discontinued. When a vendor's roadmap shifts following a corporate transaction, enterprises with deep proprietary integrations face an unattractive choice: adapt to the new direction regardless of fit, or absorb the cost of a migration that their technical architecture was never designed to support.
Building Genuine Portability Before You Need It
The corrective strategy is not to avoid CDN vendors with proprietary features — in many cases, those features deliver genuine value. The strategy is to manage the boundary between proprietary and portable with deliberate architectural discipline.
This means standardizing on open log formats and exporting data to infrastructure you control, rather than relying exclusively on vendor-native analytics. It means maintaining configuration documentation in human-readable formats that can be interpreted independently of vendor tooling. It means testing multi-vendor failover under realistic conditions — not just verifying that a secondary account exists, but confirming that a complete operational transition can be executed within the timeframe your business can actually survive.
It also means conducting an honest audit of existing technical dependencies before the next contract renewal cycle. Every proprietary integration that cannot be replicated elsewhere is a constraint on your future options. Identifying those constraints during a period of stable operations is substantially less expensive than discovering them during a crisis.
The Architectural Choices That Define Resilience
Business continuity is ultimately an architectural property, not a contractual one. No service level agreement can substitute for infrastructure designed with genuine failover capability. And no multi-vendor strategy can deliver real resilience if the technical dependencies binding an organization to a single provider have never been mapped, tested, or reduced.
The enterprises that navigate vendor disruptions successfully are not those with the most favorable contracts. They are those that made deliberate architectural choices — during stable times, without the pressure of an active crisis — to preserve their operational independence. That work is less visible than a signed contract and harder to present in a board briefing. But it is the work that actually determines whether your business continuity plan holds when it is finally called upon to perform.